
IT Specialist company division
PCI DSS certification without risks and unnecessary costs
GetPCI supports businesses that work with payment data: from initial assessment to obtaining a certificate and annual recertification.
Why we are trusted
PCI DSS certification is a responsible step that requires accuracy, experience, and a systematic approach. We take care of audit preparation and subsequent support:
Experience
We identify weaknesses even before the inspection and eliminate vulnerabilities – to optimize processes and save you time.
Ready-made solutions
We provide ready-made document templates and advise on setting up information systems to take the burden off your team.
Post-certification support
We continue our cooperation after receiving the certificate – we conduct regular scans and checks to ensure that your protection remains up-to-date and meets all PCI DSS requirements until the next annual certification.
Expertise in numbers
11 years of experience in information security, payment infrastructure, ASV scans, pentests and development of regulatory documentation. 40–50 audits and consulting projects per year. Client geography: Europe, Middle East, Canada, etc.
Confirmed team qualification
Regulatory audits: PCI SSC QSA, ASV, QPA, 3DS Assessor, SWIFT CSP Assessor, CISA, CISSP, ISO 27001 Lead Auditor / Implementer.
Red Teaming & Pentest: OSCP/OSCP+, CRTP, CRTE, eWPTX v2.
Protecting cloud environments: AWS Academy Cloud Security, CompTIA Cloud+, Microsoft Certified Technology Specialist.
Network Security and Operations: Cisco CCNA Security / CyberOps Associate, CompTIA Security+ CE.
By choosing GetPCI, you get confidence in the result and a reliable partner who supports you not only during certification, but also after it.
About GetPCI
GetPCI is a specialized direction of IT Specialist. We support businesses that work with payment data and help them pass certification audits within the specified deadlines and with minimal costs.
We work with businesses that process payment data and are required to comply with international security standards. Our clients include banks, fintech companies, e-commerce, processing centers, data centers, and any organizations undergoing certification audits and requiring expert support at all stages.
We are trusted by both small companies with 10 employees and corporations with over 25,000 employees. We are proud that almost 100% of our customers return to us for recertification and with new projects – this is the highest evaluation of our work.
GetPCI
PCI DSS and payment data security
IT Specialist
Broad cybersecurity expertise
Our services
Full cycle of preparation and passing of certification audits.
PCI 3DS / PIN Security
Audits for payment services and PIN data protection in accordance with PCI SSC requirements.
SWIFT CSP
Assessing compliance with the SWIFT cybersecurity program for financial institutions.
Development of IS regulatory documentation
Preparation of regulatory documents on information security in accordance with the requirements of standards.
Need help choosing a service?
Tell us about your business — we will select the right set of audits and certifications.
Why choose GetPCI
We identify vulnerabilities for verification
We eliminate weaknesses even before the audit to optimize processes and save you time.
Ready-made document templates
We provide templates and advise on setting up information systems.
Post-certification support
Regular scans and checks to keep protection up to date every year.
11 years of experience
In information security, payment infrastructure and regulatory documentation.
Wide range of standards
PCI DSS, ISO 27001, SWIFT CSP, NIST CSF, DORA, NIS 2, GDPR, SOC 2.
International team qualifications
QSA, ASV, ISO 27001 Lead Auditor, CISSP, CISA, OSCP.
From small businesses to corporations
Clients range from teams of 10 people to companies with over 25,000 employees.
Almost 100% recertification
Customers return to us for re-certification and new projects.
How we work
Five stages from initial consultation to final assessment and support.
Consultation
Filling out the questionnaire, choosing a procedure and estimating the cost of certification.
Volume assessment
Signing the contract and agreeing on the project boundaries and stages.
Gap analysis
Technical analysis of the infrastructure and a report with a list of non-conformities.
Implementation and preparation
Resolve discrepancies in close collaboration with your team.
Final evaluation and support
Certification audit, issuance of a certificate and annual recertification.
Industries we work with
Our experts
A team of certified PCI DSS and ISO 27001 auditors.

Anatolii Zhuravliov
Director of Audit Department
PCI DSS, PCI 3DS, SWIFT, ISO 27001, NIST CSF Lead Implementer

Anastasia Karmazina
Lead IT Auditor
PCI DSS, ISO/IEC 27001 Lead Auditor / Lead Implementer

Mykyta Rakov
Information Technology Auditor
PCI DSS, ISO 27001 Lead Auditor / Lead Implementer

Volodymyr Kostenok
Sales Manager
Project Manager, 14 years of active sales experience

Olena Pryimak
Project Manager
Project management, 10 years of experience
Certificates
Examples of certificates of conformity issued by certified auditors of our team.
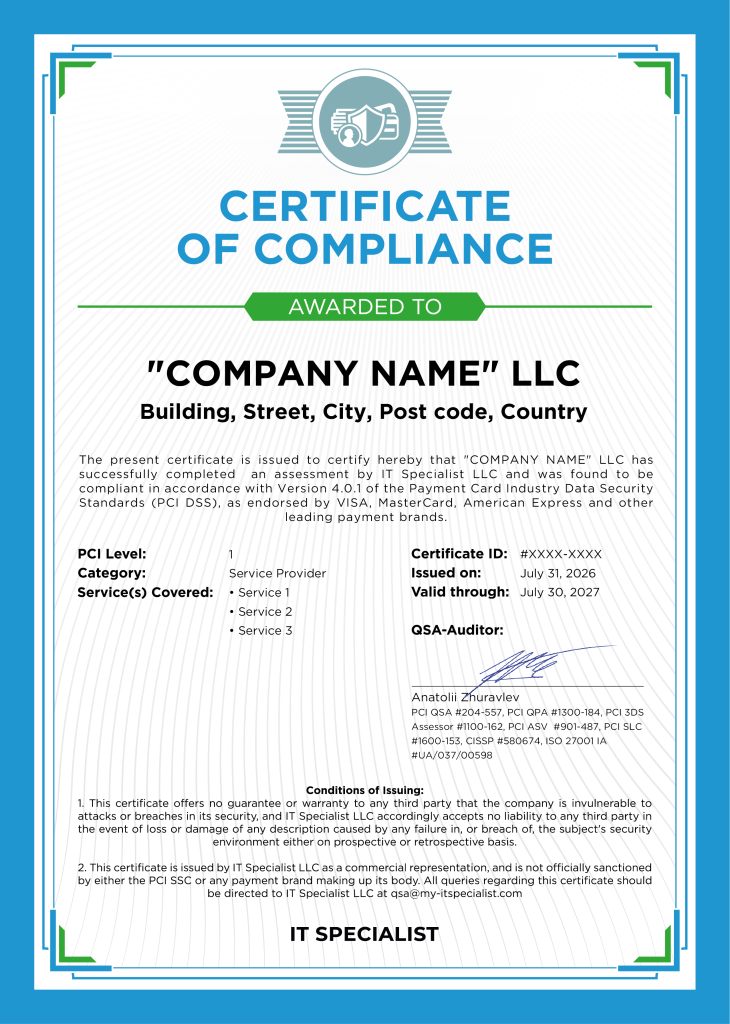
Certificate of Compliance — PCI DSS
Certificate of Compliance with the PCI DSS v4.0.1 standard, issued and signed by QSA auditor Anatoly Zhuravlev.

Certificate of Compliance — PIN Security
Certificate of Compliance with the PCI PIN Security v3.1 standard, issued and signed by QPA auditor Anatoly Zhuravlev.
Certificates are issued on behalf of IT Specialist LLC and signed by our lead auditors in accordance with PCI SSC requirements.
Ready to get certified without unnecessary risks?
Leave an application — we will conduct an initial assessment, offer an action plan, and guide you through all stages of certification.